Kleidos keeps your passwords encrypted on a small device and types them for you over Bluetooth, after you unlock it on the device itself. No app. No cloud. Nothing to sign up for.
Unlocking a device and opening an entry.A StickC Plus S3 wakes on its locked screen. A button is held four times, the arc sweeping to a different digit each time; the device derives the key, and the unlocked vault lists six demonstration services: GitHub, Google, Microsoft, Dropbox, Mastodon and Bluesky.A recording of the device's own screen: the board sent every frame over Wi-Fi as it drew it, while a script worked its controls, so the clip runs at the speed the device really runs at.
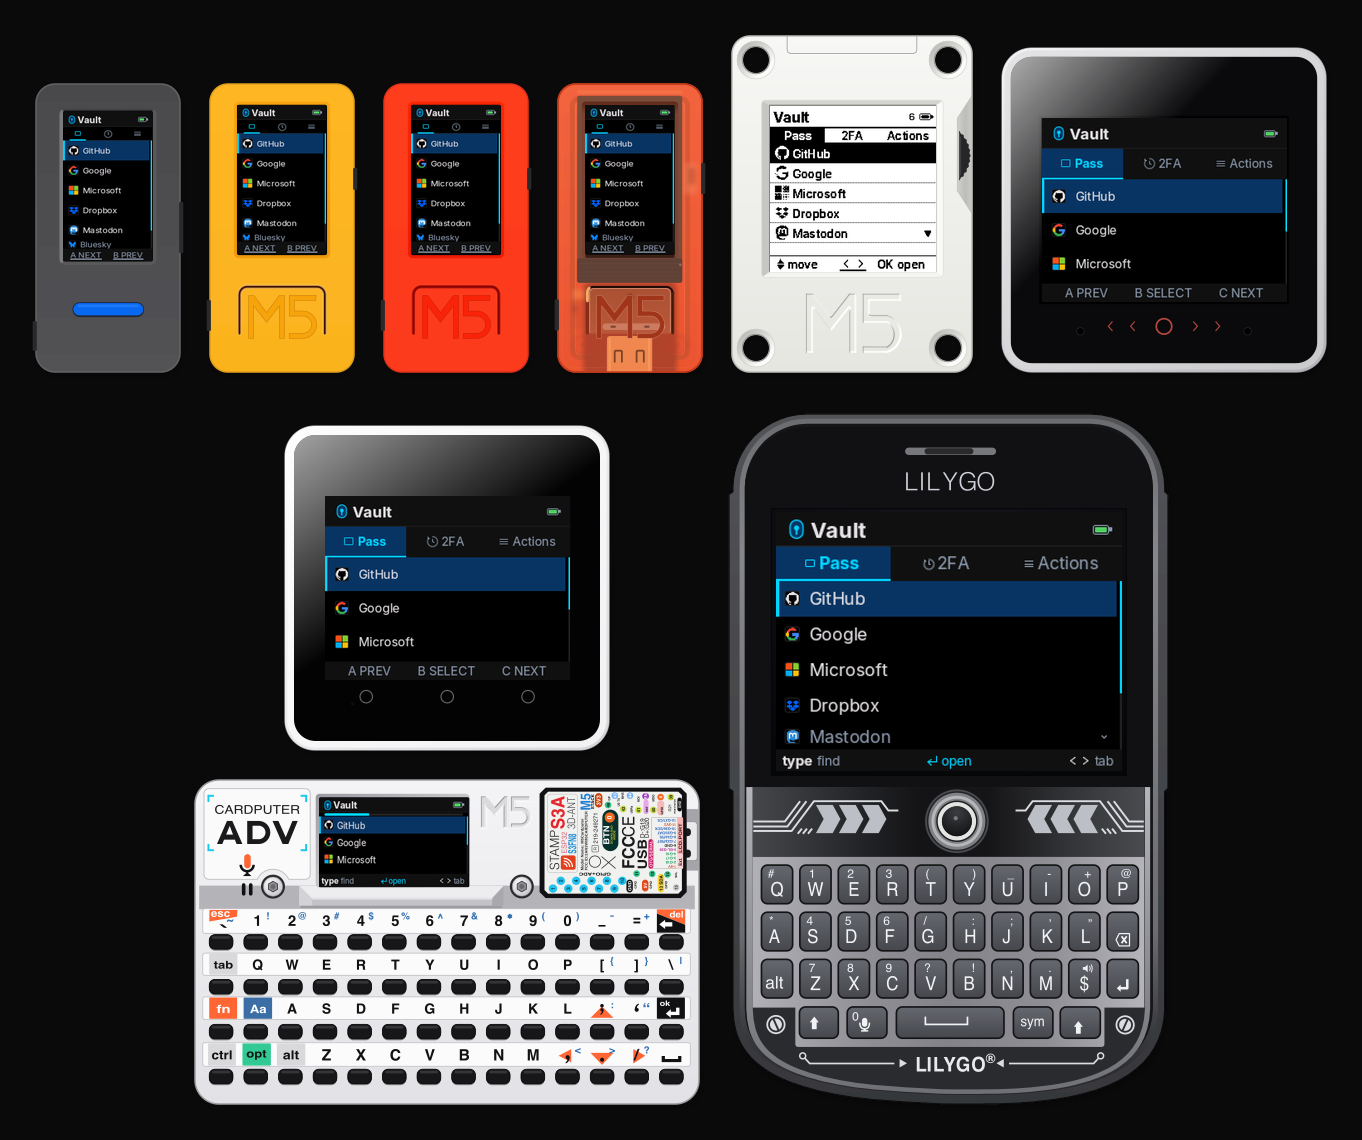
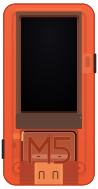
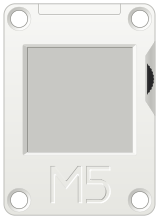
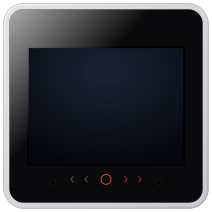
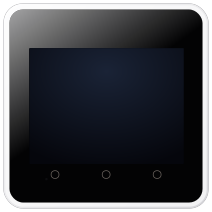
Drawing with device screensOne firmware, nine boardsDrawn to scale from each board's measured case and screen: 24 × 48 mm for the smallest, 73 × 115 mm for the largest.
How it works
1Step 1. Unlock it
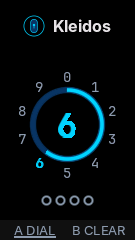
Enter your PIN on the device. The two-button models have no keypad: you hold a button while an arc sweeps through the digits and let go on yours, once per digit. A PIN is 4, 6 or 8 digits; the models with a keyboard take a passphrase instead, and the touch models let you choose one.
The PIN screen, mid-sweep. Captured from the device's own screen on a development build.
2Step 2. Pick an entry
Scroll your vault and open an entry. It draws the service's mark when it recognizes the name, and the password stays masked until you ask for it, then masks itself again.
The vault list.On the touch model a finger drags the vault list down to the last of the six demonstration services, and two taps open it: the account is shown, the password still masked.A recording of the device's own screen: the board sent every frame over Wi-Fi as it drew it, while a script worked its controls, so the clip runs at the speed the device really runs at.
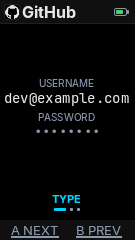
Choosing what to type.A demonstration entry is open. The chooser asks what to type — the pair, the username, or the password — the device advertises and waits for a computer, and the cancelled session shuts Bluetooth down again.Assembled from captures of the device's own screen, in the order and at the times a live run shows them.
What the Bluetooth link does
It only sends. The device is a keyboard: the one thing the computer can write back is the keyboard-LED byte, and Kleidos does nothing with it.
Pairing is LE Secure Connections only, with a six-digit number you compare and confirm on the device. Legacy pairing is not compiled in.
Keystrokes leave only over a bonded, encrypted, authenticated link with a 16-byte key, and the link is checked again immediately before every report.
The device advertises under a private address that changes every 15 minutes.
A computer that is already paired cannot quietly pair again: the device refuses and asks you first.
Bluetooth is off until you start a session — sending an entry, pairing a new computer, first-time setup — and it is shut down when the device locks or sleeps.
4Step 4. Manage it from a browser
To add, import or export entries, open the admin panel: the unlocked device puts up its own Wi-Fi network and shows a QR code. Scan it, and the panel is in your browser. The models with a keyboard can also edit entries on the device.
Security on the device
The vault is a few files on the device's own flash. Everything below is about what those files are worth to someone who takes them.
Every entry is encrypted and authenticated
A record is encrypted with AES-256-CBC and authenticated with HMAC-SHA256, encrypt-then-MAC. The tag is verified before anything is decrypted, and it covers the record's type, its slot and a counter — so a record cannot be moved to another slot, read as another type, or rolled back on its own. Password entries are all padded to the same 4 KB, so their size says nothing about what they hold.
Your PIN is never stored
The key is derived from your PIN with PBKDF2-SHA256 over a random per-vault salt: 175,000 iterations on the ESP32-S3 boards, 40,000 on the classic ESP32 boards, each sized to roughly a two-second unlock. What the device stores is a verifier, not the PIN. Encryption, authentication and the unlock check use three separate keys.
Lockout, then wipe
From the fourth wrong secret the device locks for 30 seconds, from the seventh for 5 minutes. The tenth erases the vault, every Bluetooth pairing and the admin network's identity. The attempt is written down before the secret is checked, so cutting the power does not buy a guess back.
Keys are wiped when it locks
Locking and sleeping both stop the radios and then erase the keys and the decrypted lists from memory. The buffers that held them are overwritten on purpose, not just released.
Production builds are quiet
The release and hardened builds compile no serial console and no log calls at all, and a crash prints nothing — no banner, no registers, no backtrace. The chip's own mask-ROM boot line is all that remains, and it says nothing about your vault. Passwords, usernames and PINs are kept out of logs by design.
Hardened build: in development
In development
On the 8 MB boards the hardened build adds Secure Boot v2, flash encryption and encrypted settings, and ties the vault key to the individual chip — so a copy of the flash cannot be attacked away from the device. I have not finished it: I have still to write what provisions the chip key on the ESP32-S3 boards, so a hardened build cannot create a vault there today.
The admin panel
In development
Everything in bulk — adding entries, importing from another manager, exporting an encrypted backup, updating the firmware — happens in a browser, on a network the device itself puts up. The device is the web server: nothing goes through an outside service.
The panel is in development. It is already where entries are added, imported from another manager and exported as an encrypted backup, and it is still changing: where the device draws each service's mark, the panel prints the name as text.
It opens only from an unlocked device, and only on the device's own network: WPA3-SAE with hash-to-element, protected management frames required, no WPA2 fallback, one client at a time.
By default every session draws a new 20-character password and shows it as an ordinary Wi-Fi QR code on the unlocked screen. You can choose to pin one instead.
Inside that encrypted link the panel speaks plain HTTP, with a per-session token, a Host check that blocks DNS rebinding, an idle timeout and per-address rate limits. There is no TLS on top: the Wi-Fi encryption is the transport boundary.
Wiping, deleting or forgetting a pairing asks for your unlock secret again and counts toward the same lockout. A wrong one always draws the same refusal, whether it was merely wrong, the one that started a lockout, or the one that spent the last attempt.
Bluetooth and Wi-Fi never run at the same time: each refuses to start while the other is up.
Updates, on the 8 MB boards: you upload firmware from the panel behind a second password shown on the device. An image built for another board, or an older version, is refused, and an update that boots but never confirms itself rolls back on its own.
The vault in the panel: the same six demo entries the device shows.
I opened the panel's own page — the bytes the firmware serves — in a browser against a demo vault served from this computer instead of from a board, and captured it there. The walkthrough and the rest of the captures are with the other recordings.
The devices
One firmware across nine boards, from a 24 × 48 mm stick with two buttons to a 73 × 115 mm unit with a keyboard. Which board you use changes how you unlock it and how much the screen can show; it does not change the vault.
Scale
M5StickC Plus S3
Chip
ESP32-S3
Input
Two buttons
Screen
135×240
Case
24×48 mm
Hardened build
In development
M5StickC Plus2
Chip
ESP32
Input
Two buttons
Screen
135×240
Case
24×48 mm
Hardened build
In development, chip revision 3.0 or later
M5StickC Plus 1.1
Chip
ESP32
Input
Two buttons
Screen
135×240
Case
24×48 mm
Hardened build
Not available (4 MB flash)
M5StickC Plus SE
Chip
ESP32
Input
Two buttons
Screen
135×240
Case
24×48 mm
Hardened build
Not available (4 MB flash)
M5Stack CoreInk
Chip
ESP32
Input
Dial
Screen
200×200
Case
40×56 mm
Hardened build
Not available (4 MB flash)
M5Stack CoreS3 SE
Chip
ESP32-S3
Input
Touch screen
Screen
320×240
Case
54×54 mm
Hardened build
In development
M5Stack Core2 v1.3
Chip
ESP32
Input
Touch screen
Screen
320×240
Case
54×54 mm
Hardened build
In development, chip revision 3.0 or later
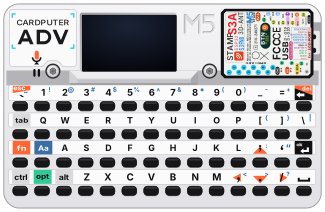
M5Cardputer ADV
Chip
ESP32-S3
Input
Keyboard
Screen
240×135
Case
84×54 mm
Hardened build
In development
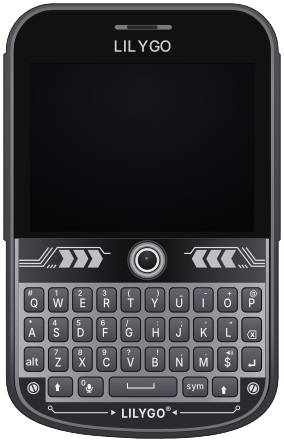
LilyGO T-Deck Plus
Chip
ESP32-S3
Input
Keyboard
Screen
320×240
Case
73×115 mm
Hardened build
In development
Each board is drawn from its own measured case and screen dimensions, not from a photograph. Pictures and recordings of the real screens are on the in-use page.
Screens are shown in English. The device itself also speaks Spanish, French, German and Italian.
Kleidos is an independent project, not affiliated with M5Stack or LilyGO. Product names are their owners' trademarks.
The whole of it, honestly: what works, what is being built, and what has not been started. Each row names what makes it true.
Working
One firmware, nine boards
Every board registers its own hardware — its screen, its power controller, its buttons or keyboard — into the same firmware, and the drawings in “The devices” are generated from the same measured boards (src/boards/).
Working
The encrypted vault on the device
Entries are stored as encrypted, authenticated records, with separate keys for encryption, authentication and the unlock check, and the host test suite covers the round trip and the refusals (src/vault/).
Working
Unlocking, on every kind of input
The two-button boards dial a PIN on the timing arc, the boards with a keyboard take a passphrase, and the touch boards are offered either (src/ui/entry/).
Working
Typing over Bluetooth
The device becomes a Bluetooth keyboard for the session it is told to start, types over a bonded and authenticated link, and shuts the radio down again when the session ends (src/ble/).
Working
Firmware updates from the browser
On the boards with room for two app partitions, firmware is uploaded from the admin panel; an image built for another board or an older version is refused, and an update that boots but never confirms itself rolls back on its own (src/platform/ota.cpp).
Being built
The admin panel
In development. It is already where entries are added, imported from another manager and exported as an encrypted backup, and it is still changing (src/web/).
Being built
The hardened build
In development. Secure Boot, flash encryption and encrypted settings are configured for the 8 MB boards; I have not written what provisions the per-chip key on the ESP32-S3 ones yet, so a hardened build cannot create a vault there today (docs/security/secure-provisioning-checklist.md).
Not started
The power figures, measured at the cell
Every board's current is still an estimate. I have not made the bench measurements that would replace the estimates with readings from a meter, so this page quotes no power figure at all (docs/testing/production-sleep-checklist.md).
Not started
The long end-to-end run
The release criteria ask for 50 end-to-end cycles — boot, unlock, browse, type, sleep — with no crash. I have not run them, and I have ticked no other box on that list either (docs/QA_CHECKLIST.md).
Not started
The first release
There is nothing to install yet: the firmware is at version 0.1.0, no release is published, and this page says “coming soon” because that is what it is (version.txt).
Not started
Flashing a board from the browser
The page that would install the firmware over USB from a browser is written and parked: it has no release to offer, so this site publishes nothing at its address and its own manifest lists no build (web/).
Not started
A review by somebody else
I have not had the firmware or the cryptography reviewed by anybody outside the project. The dossier an auditor would start from is written and waiting (docs/security/audit-dossier.md).
I put no dates on this list. It names only work that exists in the repository, and a step nothing there can show is listed as not started.
What it does not do yet
Read this part before the rest.
Pre-release, version 0.1.0. I have not had it audited by anybody independent.
I have not got the hardened build working end to end on a device yet.
On the open builds, someone who copies the flash can try PINs offline. A longer PIN, 6 or 8 digits, or a passphrase on the models with a keyboard or a touch screen, slows that down; only the hardened build's chip binding stops it. Keep the device with you.
The admin panel trusts whoever joins its Wi-Fi network. Joining needs the one-time password on your unlocked screen, so scan that code yourself, in private.
Only the hardened build checks firmware signatures.
The departments
The project is organized the way a company is. Every department below is work that exists in this repository, and every post is held by the same person.
JMRP
Direction
Founder and director
José M. Requena Plens
JMRP
Brand and design
Creative director
José M. Requena Plens
Yes, him again.
docs/design/
JMRP
Product and hardware
Head of board selection
José M. Requena Plens
Still him.
variants/
JMRP
Firmware
Principal firmware engineer
José M. Requena Plens
src/
JMRP
Security
Cryptography architect
José M. Requena Plens
The hiring process was short.
src/crypto/
JMRP
Interface and experience
Head of product design
José M. Requena Plens
src/ui/
JMRP
Admin panel · backend
Server engineer
José M. Requena Plens
Internal promotion.
src/web/
JMRP
Admin panel · frontend
Client engineer
José M. Requena Plens
web_src/index.html
JMRP
Validation and QA
Head of quality
José M. Requena Plens
There is a career path here, too.
test/
JMRP
Hardware lab
Board test technician
José M. Requena Plens
qa/tests/hardware/
JMRP
Documentation
Technical writer
José M. Requena Plens
And the coffee.
docs/
JMRP
Release
Version manager
José M. Requena Plens
version.txt
JMRP
Compliance and licensing
Legal counsel (GPL-3.0)
José M. Requena Plens
Open positions: all of them.
LICENSE
Follow and subscribe
There is nothing to install and nothing to sign up for. Pick whichever of these you already read.
There is no repository to watch yet: I am keeping the source private while I prepare the first release, so the feed and the two accounts are the whole of it.